polski
 español
On Wednesday, October 21, several sites run by Belgian media groups DPG Media and Roularta went offline. So did the website of the Flemish Parliament. Their operators were responding to a warning about PHP, the software that runs applications on a web server. Taking a site down was a precaution they could take while arranging the fix. For a newspaper, that decision has an immediate cost: readers who follow a link to today’s lead story can’t read it. Reporting from Belgium · BBC coverage.
At 4media, the server update was ours to handle. As Piotr Marek, CEO of 4media, put it: “Our team already has patched every CMS4media site and server.” Publishers using the platform did not have to install the fix themselves.
Why a newsroom login offered no protection
The two vulnerabilities, known together as PHP2Shell, affected PHP itself. On a vulnerable server, a specially crafted web request could let someone run code without a username or password. The PHP team demonstrated one configuration in which the attack could take effect before the website’s own application code even began to run. An editor could use a strong password, keep every WordPress plugin current and still need someone to update PHP on the server. PHP’s October 21 security advisory.
That distinction matters well beyond Belgium. On November 16, W3Techs detected PHP on 68.2% of the websites for which it could identify a server-side programming language. WordPress runs on PHP. On a WordPress site, the hosting arrangement determines who can actually change the version serving readers. W3Techs usage survey · WordPress guidance on PHP and hosting.
The first attempts came before the fix
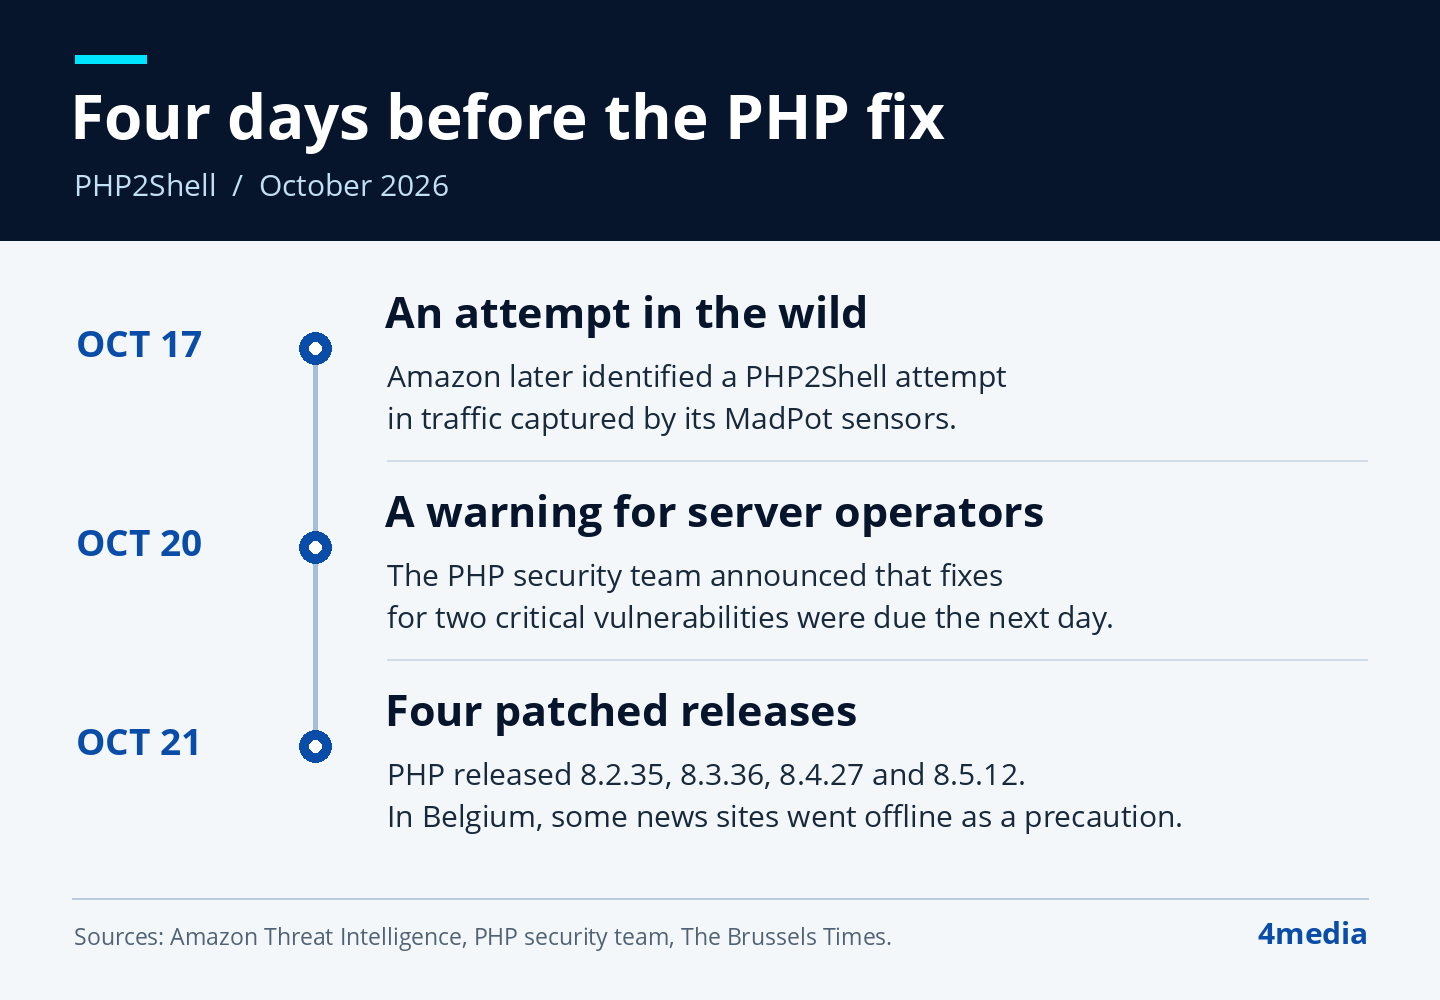
On October 20, the PHP security team told administrators to prepare for an update the following day. By the time that notice went out, someone had already tried to exploit the flaws. Amazon Threat Intelligence later identified an October 17 attempt in its MadPot network, which uses decoy systems to observe attackers. Cloudflare separately saw attackers alter the requests they sent to its customers as they tried to get past its defenses. PHP’s advance notice · Amazon’s account · Cloudflare’s observations.
Security researchers also saw traffic directed at a journalism site. Qurium, which helps protect independent media, recorded requests targeting the website of Arab Reporters for Investigative Journalism before the fixes became available. For a local publisher, the timing is the detail worth remembering. A host that had already assigned the update to an engineer could act as soon as the patch arrived. Qurium’s analysis of the requests.
What to ask the person who runs your server
“We run PHP 8.2” is only the start of an answer. The PHP project shipped the October fixes in 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Some operating-system vendors also applied the fixes to older versions they maintain. Ubuntu, for example, issued a corrected PHP 8.1 package for Ubuntu 22.04 LTS. A useful confirmation identifies the full production version or vendor package and the security update it contains. PHP release details · Ubuntu’s package notice.
If you run a small paper, you can put the whole question in one email to your host:
Which PHP build is serving our live site? When did you verify that it had the fixes for CVE-2026-109618 and CVE-2026-109619? Who handles the next critical update if it lands after hours?
Send it to the person or company with access to the production server. The developer who built the site can be the right person. What matters is whether that person still has access, has agreed to maintain it and has someone to cover an absence. If several local titles share your hosting account, ask which domains the confirmation covers.
What managed hosting meant for CMS4media publishers
CMS4media includes hosting infrastructure and dedicated vendor support. In this incident, that meant a publisher had an answer to the after-hours question before the alert arrived. Our team applied the PHP fixes across the platform. An editor finishing a school board story had no server update to schedule and no former developer to track down. What’s included with CMS4media.
If you’re comparing platforms for your newspaper, bring that same email to a demo. Ask who has the authority to patch your live site, who covers evenings and how you can confirm the work is done. We’d welcome those questions about ours. Talk to the CMS4media team.